TOPICS
Application security
Points of vigilance around websites, access, interfaces and publishing logic.
RESOURCES AND NOTES
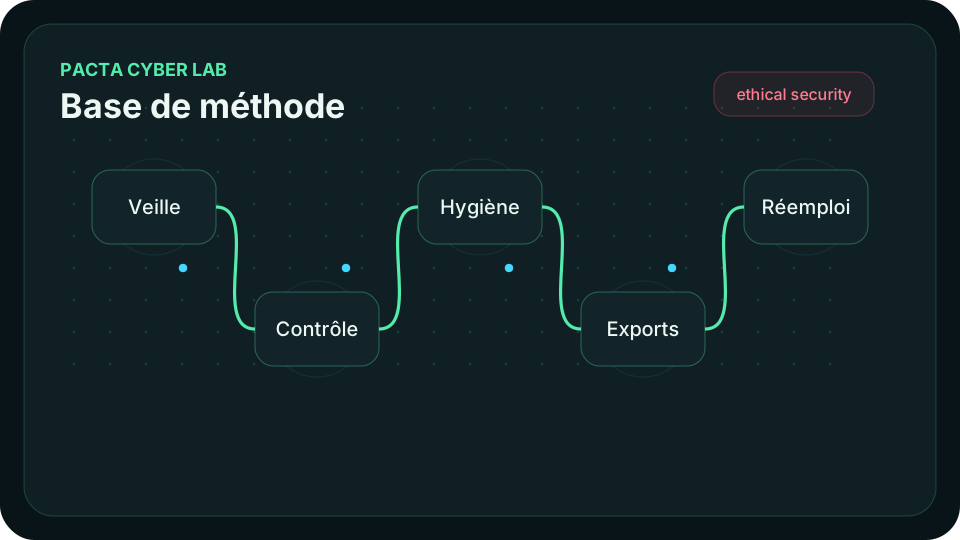
The documentation gathers notes about exposure surface, good practice, collection flows, repetitive checks, reusable exports and the methodical organisation of cyber work.
RESOURCES AND NOTES
The goal is not to multiply vague security talk, but to offer usable reference points: how to organise findings, what to monitor, how to keep outputs readable and which tasks deserve automation.
TOPICS
Points of vigilance around websites, access, interfaces and publishing logic.
Sequencing checks, preparing observations and organising working outputs.
Reasoned use of public information for monitoring, evidence or analysis.
PRINCIPLES
Provide concrete, readable and immediately useful content.
Recall the legitimate framework for usage, testing and automation.
Encourage durable methods rather than dependence on a single tool.
QUICK SEARCH
Enter a term to display only the notes relevant to your reading.
Identify what is visible, public or weakly protected before an incident reveals the issue.
Define which checks can be delegated to a workflow without removing human analysis.
Organise findings, screenshots and observations into reusable formats.
Always connect testing, monitoring and automation uses to a clear and ethical purpose.
Describe your need: website hardening, pentest awareness, automated checks, tool creation, training or technical documentation.